

Good Smile Company has taken its global online store offline after an outside party accessed customer records and order histories. The Japanese maker of Nendoroid figures disclosed the intrusion following repeated access to its administrative system between October 19 and October 22, 2026. While full payment card numbers remained safe, the company confirmed that the Good Smile data breach exposed personal contact details, purchasing records, and partial card numbers [1].
Timeline of the Good Smile Data Breach
Unauthorized visitors entered the administrative system multiple times across four days before technicians spotted the activity. Technicians detected nothing earlier. Server logs confirmed that intrusions started shortly after 3:00 PM Japan Standard Time on October 19, 2026, and continued until roughly 10:00 PM on October 22 [2].
Good Smile learned about the unauthorized access on the morning of October 23, after receiving an alert from the contractor that develops and maintains the e-commerce site. The business took the web store down promptly to stop further intrusions and protect shopper accounts. On the same day, Good Smile reported the incident to Japan’s Personal Information Protection Commission as required by national privacy rules [3].
Technicians identified a flaw in the online shop system that allowed unauthorized visitors to view administrative data. In an update released on October 26, Good Smile stated that the breach did not stem from a widely discussed PHP vulnerability, which engineers had separately resolved during scheduled maintenance between October 21 and October 22. Good Smile said it patched the suspected vulnerability and introduced additional system security measures to prevent similar compromises. The firm hasn’t publicly detailed the mechanics of the exploited bug, and forensic investigations into server logs remain active [2].
Customer Details and Payment Records Exposed
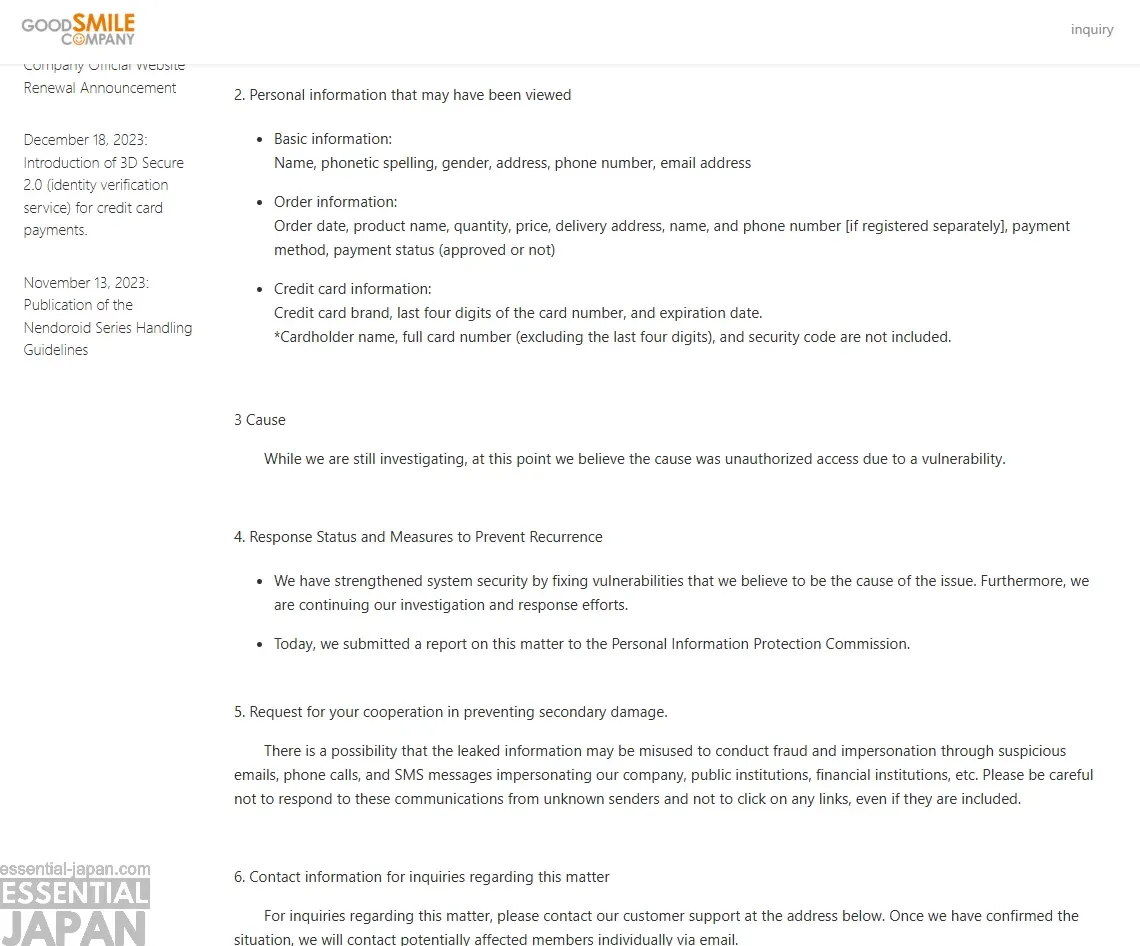
The unauthorized visitor accessed several categories of personal information stored in customer accounts. Good Smile confirmed that exposed profile records include customer names, phonetic readings of Japanese names, gender, registered mailing addresses, telephone numbers, and email addresses. The company stated that attackers also viewed order histories, which contained purchase dates, product names, order quantities, total prices, shipping destinations, and payment completion status for individual transactions [4].
Payment card information associated with store purchases was also exposed during the incident, though payment security boundaries prevented total card data theft. Intruders viewed card brands, card expiration dates, and the last four digits of card numbers entered by shoppers. No passwords leaked. Good Smile stated that full sixteen-digit card numbers, cardholder names, and three-digit card verification value (CVV) security codes were not stored on the compromised administrative server and were never accessed. In addition, transactions processed through external checkout services such as Amazon Pay and PayPal avoided card exposure because those payment credentials never passed through Good Smile’s storage [2]. The business hasn’t disclosed the total number of exposed customer accounts.
Good Smile plans to email all registered members, including former members who closed their accounts before the intrusion occurred. The company said individual notices will be distributed progressively as forensic teams confirm which specific accounts were viewed by the intruder [5].


Separate Regional Stores Remain Unaffected
Collectors who purchase items through Good Smile’s regional subsidiaries were largely insulated from the security event. Following the Tokyo disclosure, Good Smile Company US published an independent notice confirming that its storefront at goodsmileus.com was not affected by the breach. The American subsidiary operates on separate infrastructure, meaning customer accounts, payment data, and order records for US store users remained untouched [3].
Several other affiliated digital platforms and retail shops also run on separate systems and avoided exposure during the incident. These unaffected services include the Good Smile Company Europe Online Shop, Good Smile Company UK, the brand’s official marketplace outlet on Rakuten, and the custom Nendoroid Face Maker service. However, American and European collectors who placed orders through the global domain at goodsmile.com fall under the scope of the Tokyo store investigation [2].
The division between regional storefronts is particularly significant for international hobbyists who hold active logins on both websites. Good Smile previously suspended direct shipments from Japan to the United States in April and August 2025 due to logistical hurdles, prompting many overseas collectors to register on both the global and American shops. Good Smile US reminded shoppers that having an unaffected American account does not protect personal records stored on the global site if a buyer placed orders through both portals. The American branch advised collectors to use unique passwords and said that official representatives will never ask for passwords or complete credit card numbers by email [3].
Phishing Risks After the Good Smile Data Breach
While full payment credentials remained unexposed, the leak of customer identities and order logs creates phishing risks for shoppers. Fraudsters often use stolen names, email addresses, and detailed order histories to craft deceptive messages that appear genuine. Scammers can cite real product preorders, shipping addresses, or past payment methods to trick collectors into sharing credit card numbers or account passwords [2].
Good Smile cautioned users to remain watchful for suspicious emails, telephone calls, or text messages claiming to come from the manufacturer or financial institutions. Customers shouldn’t click unexpected links and should verify any account requests through official customer service channels [4].
On social media, figure collectors voiced frustration regarding repeated security issues across hobby platforms. Online discussions on X pointed to earlier security incidents on related sites in 2024 and 2025 as part of an unsettling trend. Following the Good Smile data breach, several buyers expressed reluctance to place direct preorders in the future, urging manufacturers to invest more heavily in third-party penetration testing and continuous infrastructure monitoring [6].
Ongoing Investigation and Store Status
Despite the storefront shutdown, Good Smile confirmed that back-end warehouse logistics and order fulfillment remain functional. Staff continue to prepare and dispatch existing purchases and preorders scheduled for shipment during October. The company stated that preorders affected by payment errors while the shop is offline will not be canceled automatically, giving customers time to resolve billing questions with support agents [2].
Shoppers who need to update order details or close their store accounts can use the official customer support inquiry form. Support teams remain available. Because that support portal functions on separate servers independent of the online shop, requests continue to be received and processed normally [3].
Good Smile is widely known in the entertainment sector as a manufacturer of hobby merchandise, toy figures, and anime adaptations. The company built international prominence through its articulated figma line and its popular Nendoroid series, which offers stylized collectible figures with swappable faces and accessories. These collectibles enjoy a large global fan base, making the official shop a key purchasing channel for collectors worldwide [1].
The company hasn’t announced when the global online store will reopen for new orders. Good Smile stated that the store will stay offline until security specialists complete forensic reviews and verify that all system vulnerabilities have been eliminated. As technicians work to finalize their review of the Good Smile data breach, the manufacturer continues cooperating with Japanese regulatory authorities to strengthen defenses across its digital platforms [2].
- ONLINE NEWS Anime News Network. (2026, October 28). Good Smile Company announces data breach of online store. [Article Link]
- ONLINE NEWS Gonzales, M. (2026, October 27). Good Smile Company data breach: Customer details exposed, store shut down. Esecurity Planet. [Article Link]
- ONLINE NEWS Davis, C. (2026, October 24). Good Smile Company shuts down official online store after major security incident. Essential Japan. [Article Link]
- ONLINE NEWS Keshino. (2026, October 24). Good Smile Company: Member information may have leaked after unauthorized access to official shop—site closed as cause is investigated. Game*Spark. [Article Link]
- WEBSITE Aawa Technologies. (2026, October 23). Good Smile Company: Unauthorized access to the Official Shop. JapanHacked. [Article Link]
- WEBSITE X. (2026, October 23). Good Smile Company warns of online store data breach. [Article Link]


