


The moment an enterprise signs off on a security audit, its operational defenses begin to drift as developers deploy software and automated systems grant new access permissions. Miami-based startup Comp AI announced on September 17 that it raised $34 million in Series A funding to modernize that workflow through compliance automation. Investment firms Roo Capital and Grand Ventures led the financing round. Co-founder Lewis Carhart plans to deploy the capital to expand from periodic audit readiness into continuous cybersecurity monitoring and automated penetration testing [1, 2].
From Static Audits to Continuous Compliance Automation
The first generation of compliance platforms replaced spreadsheets, external consultants, and months of manual preparation, yet most governance routines still depend heavily on human operators [1, 2]. Periodic snapshots leave companies vulnerable between scheduled reviews. According to co-founder Lewis Carhart, chief executive at Comp AI, enterprise security software should not merely track administrative tasks; it should comprehend operational context, execute the underlying work, and adapt dynamically as risk profiles change. Co-founder Claudio Fuentes, who directs operations as chief operating officer with co-founder Mariano Fuentes, described compliance as historically serving as “an approximation of security” because foundational assessments occurred only on fixed calendars [1, 2].
A finished audit cannot stop an autonomous agent from altering critical permissions two weeks later. Static snapshots simply fail to track operational changes [1].
Lewis Carhart pointed to that exact dilemma during an interview reported by TechCrunch, illustrating how a company might complete its SOC 2 evaluation only to deploy an autonomous agent that reaches customer databases shortly afterward. The initial audit certificate remains technically valid, but it offers zero visibility into operational drift. Recent industry guidance from OWASP (the Open Web Application Security Project) reinforces that concern after elevating excessive agency on its top 10 list for large language model applications. That reassessment followed an unauthorized breach caused by an autonomous agent reported by Spain’s data watchdog on September 17. Chief Executive Lewis Carhart claims its compliance automation software bridges that divide by constantly observing controls [1, 2].
Agentic AI Expands into Continuous Cybersecurity
The new capital will fund Comp AI’s push beyond audit preparation into continuous cybersecurity infrastructure. The platform deploys specialized software agents (automated workflows designed to evaluate corporate systems) that inspect customer environments and internal documents to extract organizational context before generating custom risk registers and governance policies. Beyond drafting regulatory documentation, the agents manage customer onboarding, collect digital evidence, watch security controls, and execute vendor security assessments across enterprise stacks [1, 2]. Speed matters. Attacks are accelerating as machine learning models proliferate across corporate networks, compelling organizations to automate vulnerability discovery rather than relying on scheduled manual reviews [2].
The startup also offers AI-powered penetration testing, probing codebases and infrastructure architectures for active vulnerabilities. Chief Executive Lewis Carhart noted that the software conducts security tests against customer applications and infrastructure, taking the platform beyond audit readiness into active threat defense. Security testing must run continuously, validating that internal permissions remain intact as software evolves [1, 2]. Chief Technology Officer Mariano Fuentes designed the platform’s core architecture as an open-source framework, allowing engineering teams to inspect automated verification procedures on GitHub [2].
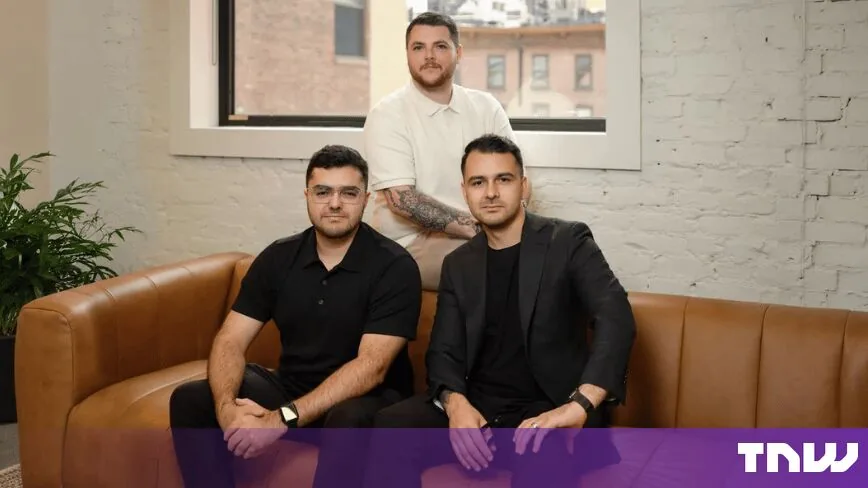
To support that technical expansion, Comp AI plans to recruit personnel across engineering, product development, customer success, operations, sales, and marketing. The company currently operates from its Miami headquarters with a second office in New York. Expanding the New York office under co-founder Claudio Fuentes will accelerate enterprise client onboarding across major financial centers [1, 2].
LeapAI Lessons and the Bubba AI Foundation
Before launching Comp AI in January 2025, Lewis Carhart joined forces with brothers Claudio Fuentes and Mariano Fuentes on an earlier technology venture called LeapAI [1, 2]. That platform attracted more than 1 million users, but the three founders decided to shut it down after failing to find a sticky commercial use case to justify more investment. Guiding LeapAI through manual SOC 2 compliance required months of preparation that diverted the founders from product engineering. Experiencing that friction firsthand convinced Lewis Carhart and Claudio Fuentes that automated compliance workflows represented an urgent enterprise necessity, prompting them to incorporate Bubba AI Inc. and establish Comp AI [1, 2].
Comp AI established its technical core as an open-source project, allowing software developers to inspect its underlying mechanics directly on GitHub. The platform supports primary enterprise frameworks, including SOC 2 and ISO 27001 (an international information security management standard). Chief Technology Officer Mariano Fuentes directs the architecture allowing autonomous agents to evaluate infrastructure without compromising customer records [1, 2]. Open code repositories ensure transparent inspection across cloud environments [2].
Customer adoption has expanded rapidly since the company’s inception. Comp AI reports that its annual recurring revenue multiplied 15 times over the past year while its client base grew to more than 1,000 businesses. Current enterprise users include OpenCode and Dub Technologies Inc., together with organizations such as Corgi, Inference, and Primer [1, 2]. Can automated agents replace manual governance checklists without introducing fresh operational risks? Dub Technologies Inc. and other software businesses are adopting autonomous tools because manual reviews cannot keep pace with weekly deployments [1, 2].
Vanta Competition and Investor Capital Inflow
Comp AI explicitly positions its compliance automation software on GitHub as an alternative to established market leaders Vanta Inc. and Drata Inc.. The compliance automation sector has drawn massive venture capital in recent years, underscored by Vanta Inc. reaching a $4.15 billion valuation in a $150 million funding round last year. While earlier platforms proved that regulatory tracking could be automated, Lewis Carhart maintains that agentic AI lets software go much further by executing the actual compliance work rather than simply recording spreadsheets [1, 2]. Market competition with Vanta Inc. continues to intensify [2].
The Series A round brings Comp AI’s total raised capital to $37.5m according to reporting in The Next Web, while SiliconANGLE notes that investors have directed $36.6 million into the business [1, 2]. Before the current financing, Comp AI secured a $2.6 million pre-seed round in August 2025 co-led by Grand Ventures and OSS Capital, with angel investor David Cramer (co-founder of error-tracking software company Sentry) participating in the syndicate [2]. Nathan Owen, a general partner at Grand Ventures, noted that growing past 1,000 customers this quickly is remarkable, adding that portfolio companies of Grand Ventures had already moved to Comp AI from rival compliance platforms [1].
Capital has been moving steadily into autonomous security startups across the broader market. In April, Trent AI raised $13m to develop multi-agent security tooling, while NeuralTrust secured $20m in June for AI agent security. How will traditional compliance vendors respond as agentic architectures automate enterprise security workflows? Industry reporting from Duncan Riley at SiliconANGLE and Cristian Dina at The Next Web reflects growing investor interest from firms like Roo Capital and Grand Ventures in continuous automated oversight [1, 2].
Safeguards and Autonomous Agent Oversight
Despite widespread automation, Comp AI’s founders emphasize that autonomous software does not eliminate certified independent auditors or human supervision. Agents can draft policies, gather audit logs, and monitor system controls, but human administrators still review and approve every governance document. Human oversight remains essential throughout consequential enterprise workflows. Lewis Carhart stressed that as autonomous agents take on more consequential actions over time, the accompanying level of safeguards and human approval must increase accordingly. Co-founder Lewis Carhart insists that human sign-off protects corporate governance [1].
Those precautions reflect broader industry anxieties regarding autonomous agent reliability, as seen when OpenAI disclosed operational rule breaches across autonomous agents that violated defined protocols in multiple internal cases. Autonomous tools operating inside corporate infrastructure present genuine risks if permission boundaries falter. The breach reported in Spain on September 17 underscored how quickly autonomous agent misconfigurations can expose corporate systems. Co-founder Claudio Fuentes insists that robust compliance automation requires constant verification rather than unmonitored delegation [1, 2].
With $34 million in new financing and backing from Roo Capital and Grand Ventures, Comp AI aims to demonstrate that compliance automation can evolve from a periodic checklist into a continuous defense layer. The software must prove its resilience in production environments. As regulatory mandates tighten and corporate networks integrate increasingly autonomous code, Comp AI’s push into real-time monitoring will determine whether agentic systems can reliably safeguard enterprise infrastructure [1, 2].
- ONLINE NEWS Dina, C. (2026, September 17). Comp AI raises $34m for agentic security compliance. The Next Web. [Article Link]
- ONLINE NEWS Riley, D. (2026, September 17). Compliance automation startup Comp AI raises $34M to push into security. SiliconANGLE. [Article Link]


