



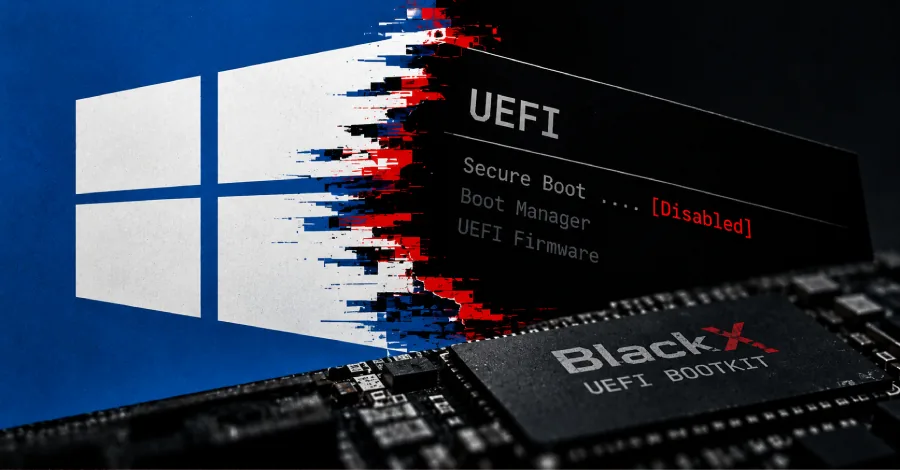
The BlackX UEFI bootkit targeted diplomatic agencies in Central Asia during a spying campaign in early 2026, evading Unified Extensible Firmware Interface (UEFI) Secure Boot defenses on patched Windows systems. Kaspersky discovered that hackers exploited the Baton Drop CVE-2022-21894 flaw to disable firmware checks before Windows boots. The intrusions hit foreign embassies in Tajikistan, Uzbekistan, and Turkmenistan, with analysts linking the attacks to Chinese threat group APT41. [2]
Connections to BlackLotus
Kaspersky researchers Georgy Kucherin, Vladimir Nestor, and Vasily Berdnikov found direct code links to BlackLotus, a crimeware bootkit seen on hacker forums in October 2022. ESET confirmed BlackLotus in March 2023 after finding it could infect patched Windows 11 PCs through CVE-2022-21894. According to Kaspersky, the exploit setup inside BlackX is “remarkably similar” to BlackLotus. [2]
BlackLotus source code leaked in July 2023. Yet investigators determined that the BlackX authors didn’t rely solely on that public leak, because when Kaspersky inspected BlackLotus samples, they found specific routines that were missing from public files but present inside BlackX. Researchers concluded the threat actors either bought private code or reverse-engineered samples. Kaspersky said state-backed groups rarely borrow tools from cybercrime actors. Bill Toulas reported for BleepingComputer that the operators used this repurposed firmware code to spy on government targets in Tajikistan, Uzbekistan, and Turkmenistan after breaching networks through an unknown entry path. [1]
Analysts connected the intrusion set to APT41, a Chinese state-sponsored actor also called Brass Typhoon, Wicked Panda, and Barium. ESET reported in June 2026 that an APT41 subgroup named FishMonger, also known as Aquatic Panda and Earth Lusca, used a Windows backdoor called SprySOCKS against government entities in Honduras, Taiwan, Thailand, and Pakistan between 2023 and 2024. FishMonger’s kernel driver shared a rare code string, “xdd”, with the driver found in BlackX. That shared string points to a common development origin among these Chinese teams. [2]
How BlackX UEFI Bootkit Exploits Baton Drop
The attack exploits Baton Drop, a Microsoft Windows startup flaw tracked as CVE-2022-21894 with a CVSS score of 4.4. To start the infection on a PC where they already hold admin rights, hackers drop an installer named inst.exe with an encrypted file called PVMDIJGKAX2. The installer runs through the command line as C:\ProgramData\Intel\inst.exe PVMDIJGKAX2 Q46F6MDLI3RX2KV1, using the string Q46F6MDLI3RX2KV1 as an RC4 key to decrypt files before copying them to system and UEFI partitions. [2]
Once those files reach the firmware disk, the exploit enrolls custom Machine Owner Keys MOKs to load arbitrary EFI files without tripping Microsoft Secure Boot protections. Microsoft said Baton Drop abuse serves as “primarily a persistence and defense evasion mechanism” rather than a way to gain initial access. Hackers can’t plant the bootkit without first having admin rights or physical access to the device, but once active, the malicious code runs before Windows starts and survives complete operating system wipes. The infection stays in non-volatile firmware memory even if IT staff replace the system hard drives. [1]
To run second-stage tools on the host, the hackers use DLL sideloading. The bootkit drops a legitimate copy of googleupdate.exe to load rogue code under a trusted Google name. Georgy Kucherin said, “By adapting a commercial crimeware tool, the group could bypass procedures intended to protect the Windows boot processes,” helping the crew stay hidden on diplomatic systems. [2]
Kernel Driver Tactics
After bypassing firmware checks, BlackX drops a Windows kernel driver signed with a cert issued to Wenjiang District Mingyu Network Technology Service Studio, which was later revoked but still loads because targets lack revocation rules. Once active, it blinds defensive monitoring tools. The driver stops security tasks, deletes registry callbacks, and tampers with Event Tracing for Windows ETW providers. This setup mimics a bring your own vulnerable driver (BYOVD) attack, where hackers use signed code to tear down host defenses from kernel space, protecting disk files by launching the Windows Calculator whenever a user tries to open them. [1]
Kaspersky found that some driver routines were coded to run only if the PC had security tools from Kaspersky or Avast installed. But Kaspersky said these evasion tricks failed against its defenses. If IT staff try to open the malware files manually, the driver opens the Windows Calculator instead. It stops defenders from easily seeing the bootkit files on disk. [1]
By seizing kernel control during boot, the driver hides all subsequent spying payloads from view. Security teams face tough odds when code runs beneath Windows, because defensive agents assume the firmware layer is clean and can’t check driver hooks placed before the kernel starts. The hackers turned that trust into a hidden foothold inside Central Asian government offices. [2]
BlackX UEFI Bootkit Secondary Payloads
BlackX deploys two spying tools. The first tool is a RAT built to run extra .NET payloads on victim systems. To hide command traffic inside daily enterprise web activity, this RAT connects through cloud services, including Google Drive, OneDrive, and Yandex.Disk. Hackers use these cloud drives to send new commands and pull stolen files from infected government computers without alerting network sensors. [1]
The second payload is OxiDLLRunner. This tool is an OLLVM-obfuscated DLL sideloaded by googleupdate.exe to decrypt v8_context_snapshot.bin and run shellcode. It loads a Rust payload. That Rust tool reaches out to a remote server at archivetj[.]com, pulling extra DLL plugins and running their create_plugin functions in separate threads to tailor spying tasks for each victim PC. [1]
These findings match patterns noted by ESET in June 2026, when researchers tied SprySOCKS activity to CVE-2023-24932, another flaw tied to BlackLotus. The fact that BlackX reuses core code from BlackLotus reveals how state-backed espionage groups repurpose crimeware to build durable firmware implants. By pairing firmware exploits with cloud C2 channels, APT41 kept quiet access while gathering intelligence on Central Asian diplomats. [2]
The Revocation Gap
All agencies hit by BlackX ran fully updated Windows builds, yet the bootkit worked because admins didn’t apply optional revocation steps. Kaspersky said the patch for Baton Drop was built to revoke the Windows Production PCA 2011 cert used to sign vulnerable boot files. But Windows does not apply this revocation on its own when an update installs. Admins must trigger the blocklist. Kaspersky noted that this gap gave hackers room to deploy their bootkit against targets that assumed their PCs were safe. [1]
The “Windows Production PCA 2011” certificate expired on October 19, 2026, but experts warned that expiration alone won’t block bad files. Vulnerable boot binaries can still execute unless defenders add the cert to the Secure Boot UEFI Forbidden List DBX. Researchers Georgy Kucherin, Vladimir Nestor, and Vasily Berdnikov said threat actors took advantage of this unpatched gap, putting work into copying BlackLotus because they knew few groups apply manual revocations. [2]
To stop Baton Drop attacks, admins must manually update the DBX list to ban vulnerable bootloaders. Enterprise IT teams tackled similar update hurdles when Microsoft delivered an emergency update to stabilize Windows 11 during earlier system patch maintenance rollouts across customer devices. Without applying the DBX blocklist, standard Windows security updates leave a firmware hole that lets bootkits like BlackX bypass Secure Boot entirely.
- ONLINE NEWS Toulas, B. (2026, October 24). BlackX UEFI bootkit exploits Baton Drop flaw to bypass Secure Boot. BleepingComputer. [Article Link]
- ONLINE NEWS The Hacker News. (2026, October 24). BlackX UEFI Bootkit Bypasses Secure Boot on Patched Windows Systems Missing Revocations. [Article Link]


